Starter
Start free with access requests and approvals.
Just-in-time access governance
Warser gives people access for as long as the work takes, removes it on the date, and writes the record as it goes.
Free Starter plan. No card required. For IT and security teams of 100 to 2,000 people.
Example organisation
3 live
14:02:11access.removedsalesforcet.reyesreason=end_date
Every joiner, move, contract and project leaves permissions behind. For the team that has to answer for them, four things go wrong.
Asked in a sentence, in the app or in Slack, and routed to the person who can say yes.
Every decision is kept with who made it, what it granted, why, and until when.
Every grant has an end. Warser removes it then, or tells a person exactly what to remove.
Reviews put every holder in front of the owner, with anything past its end date in one place.
The film follows an access request from approval and provisioning through review and removal as a person's work changes.
Spoken: People join. Roles change. Contractors leave. But their access to your systems and tools doesn't always keep up. Warser manages who gets access, who approves it, and when it needs to go. Request, grant, review and remove access in one place. The right access. For the right people. For as long as they need it.
On screen: The words "People change." and "Access doesn't." appear over three people events — a joiner, a role change and a contractor — whose access to GitHub, Salesforce and Notion stays behind after they have moved on. A Warser access request opens, showing what is being asked for, who approves it and when it ends, and the request is submitted. The approver's view appears, the request is approved, and the lifecycle settles one state at a time: requested, approved, live, removed on time, with the end date visible throughout. The film closes on the Warser mark and the line "The right access. For the right people. For as long as they need it."
From the first request to the last permission removed, keep the decision and the work together.
Capture what someone needs, what it is for and when it should end.
Route the request to the right approver, with the context to make a decision.
Grant access in connected systems with write access, or track the handoff to someone who can.
Check whether access is still needed as people, roles and work change.
Remove access at expiry where Warser has write access. Track manual removal everywhere else.
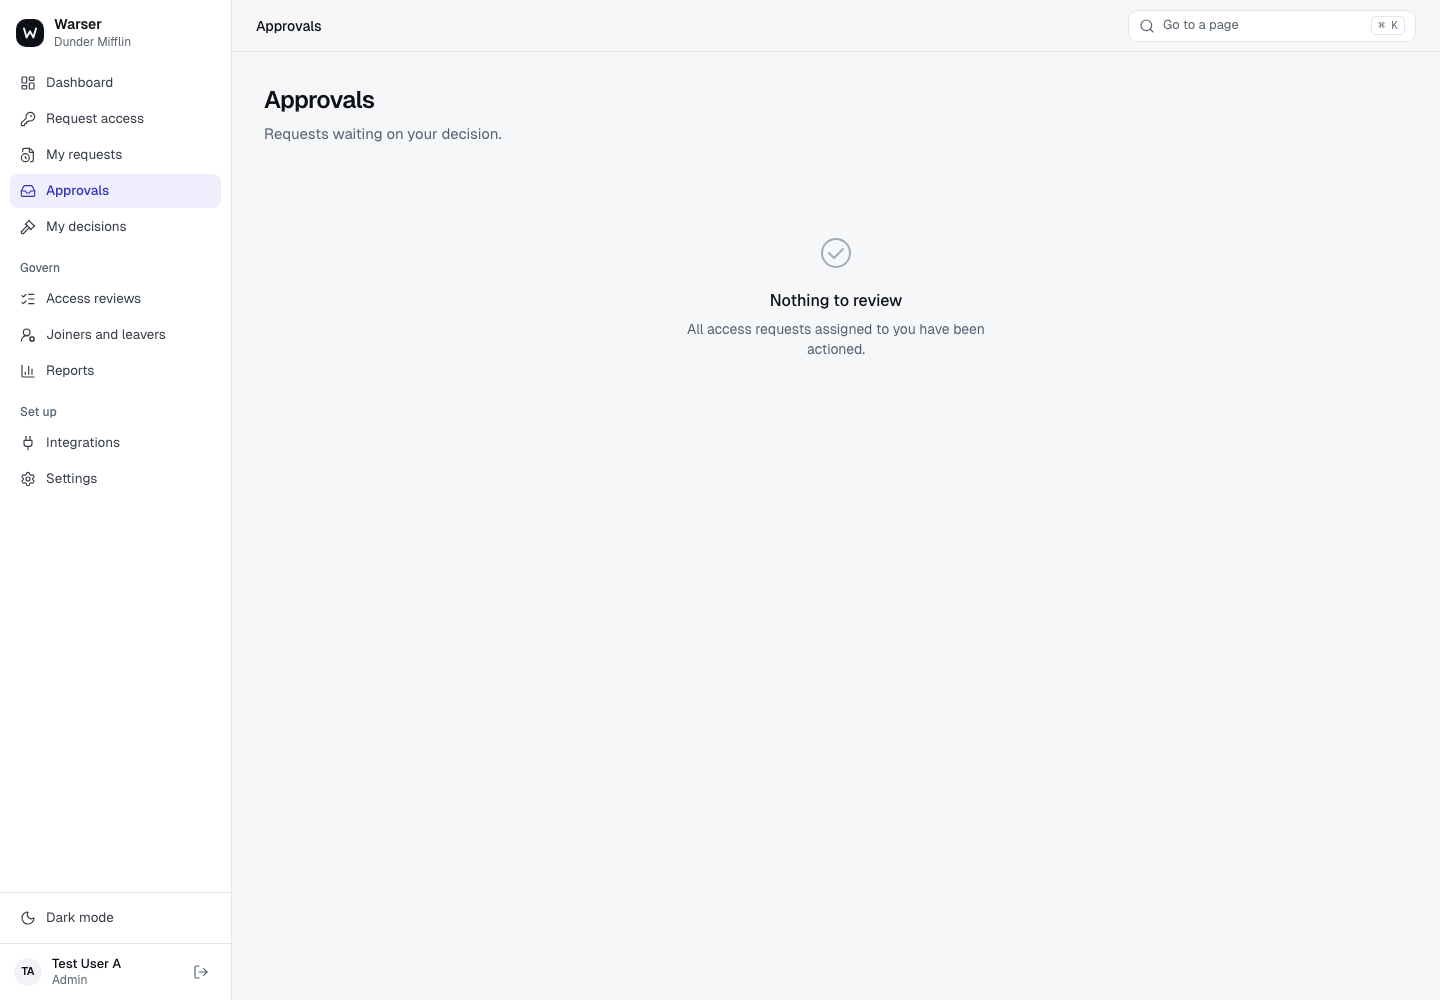
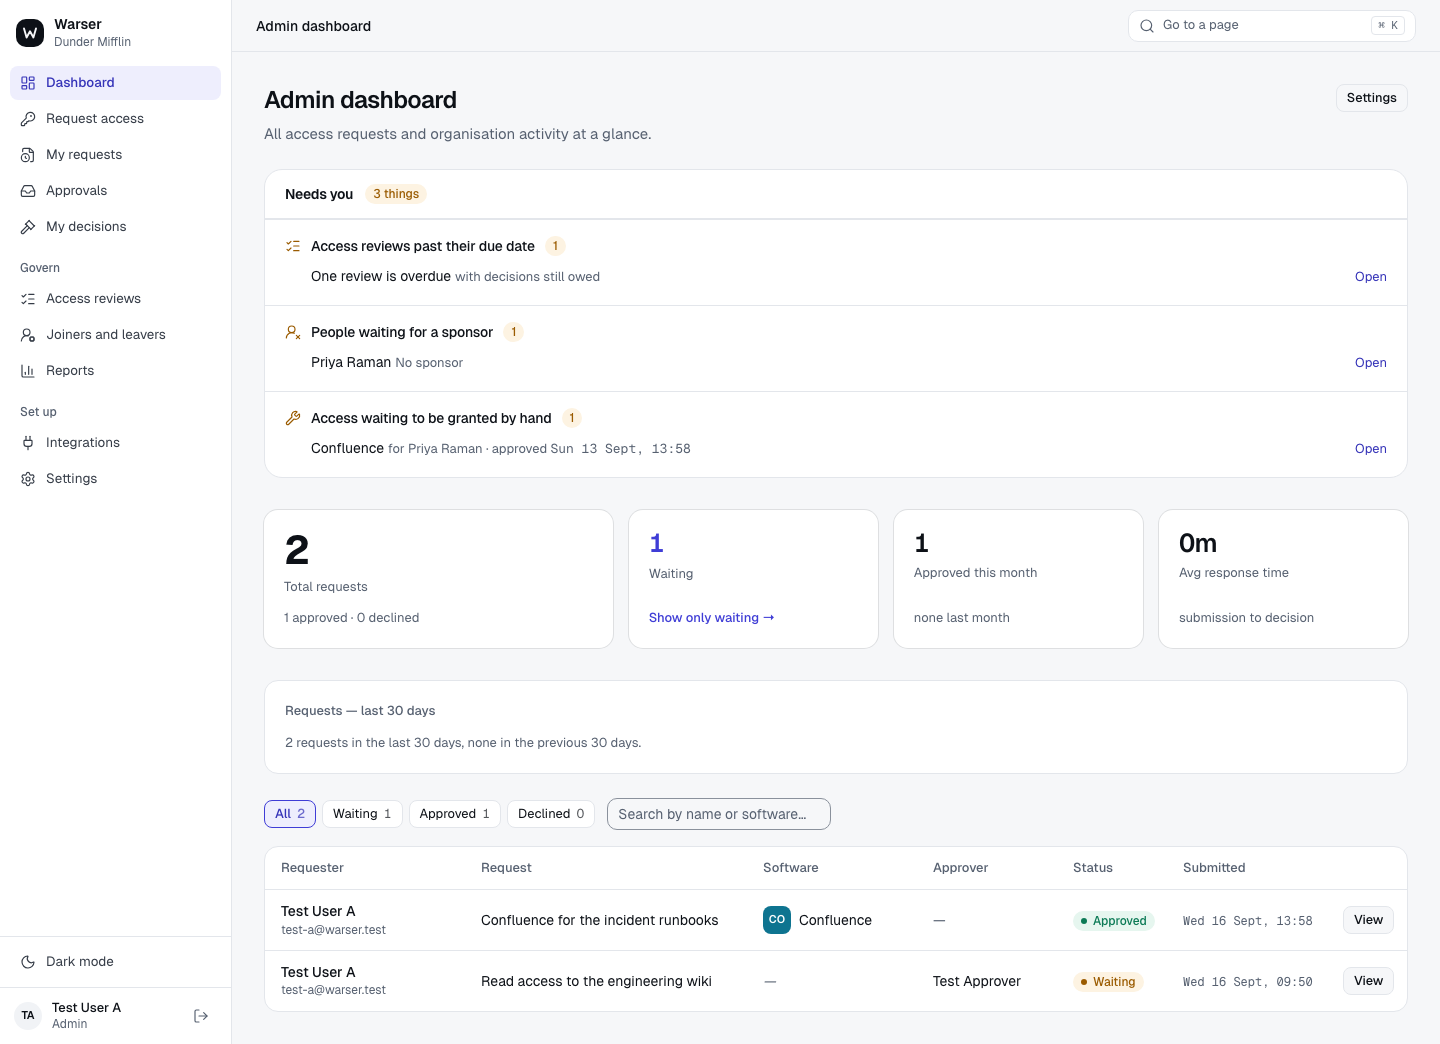
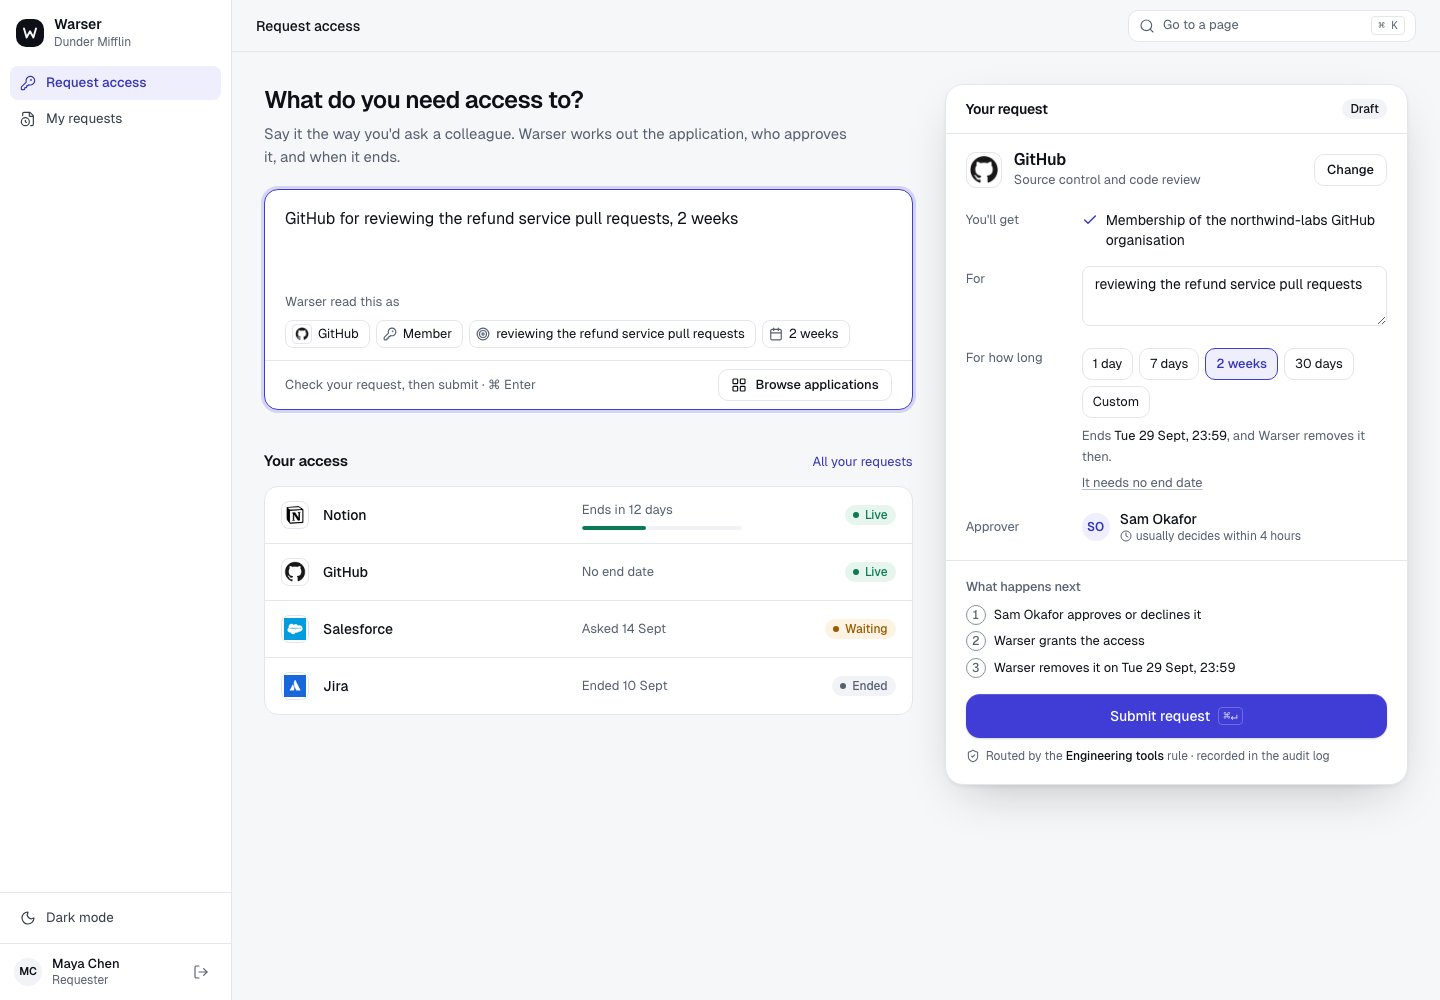
Know the purpose, approver and end date before access is granted. Give people access for the work, with a clear plan for when it ends.
When access expires, Warser removes it automatically in supported connected systems where it has write access. For other systems, removal stays visible as work for your team to complete.
Access should exist only while the work does. Warser is designed so a grant could last thirty seconds and happen two hundred times a day: the pace automated work will ask of every access system.
Live at this pointRemoved on time
Nobody holds access they are not using. It opens for the work and closes after.
Who decides, what is granted, and what a person must still do. Never a forecast dressed as a promise.
Doing the work writes the record. Nobody assembles it the week before the audit.
Every request, decision, grant, review and removal is recorded as it happens, ready for a SOC 2 or ISO 27001 evidence request, your security monitoring, or a question from a customer's security team.
Example events from a single day.
| Time | Event | Detail | By |
|---|---|---|---|
| 09:14:02 | Request made | GitHub · write to payments-api · until 29 Sept | Priya Shah |
| 09:31:40 | Approved | Routed by the Engineering tools rule, with the reason recorded | Sam Okafor |
| 09:31:41 | Granted | Added to payments-api-write in GitHub | Warser |
| 11:05:17 | Review decided | Salesforce review · 14 kept, 2 removed | Ana Duarte |
| 14:02:11 | Removed | Salesforce admin · end date reached | Warser |
| 14:02:12 | Sent to SIEM | Batch of 3 events in OCSF | Warser |
| 16:40:03 | Handed off | Figma editor · Jira ticket raised for IT | Warser |
Connect the systems that grant access, the places people ask for it and the tools that carry the work forward.

Provision and remove
Grant and remove access directly through a connected GitHub integration with write access.

Provision and remove
Sync your directory and grant or remove supported access with the required write permissions.

Request and approve
Bring access requests and approval decisions into the conversations where your team works.

Track and hand off
Hand work to the people who fulfil it, with a ticket to track completion.

Export events
Send access events into the workflows your team already runs.

Export events
Send audit events to your security monitoring tools for investigation and reporting.
Direct provisioning and removal depend on the connected system and its write permissions. Tracked handoffs still need someone to complete the work. See integration availability by plan.
More people, more applications, the same team keeping it all moving. Put access control into the everyday work without building a large identity-governance programme.
Give employees a clear way to ask. Give approvers the context to decide. Give IT a view of what is live, what needs attention and what still needs to be removed.
The evidence follows the work: requests, decisions and access changes stay recorded as your organisation grows.
Start free with access requests and approvals.
Add lifecycle automation, access reviews and integrations.
Extend identity and security controls with Microsoft Entra sync, SIEM webhooks and extended audit history.
Start with requests and approvals. Build the rest of your access lifecycle from there.
Free Starter plan. No card required.